
IRDAI Compliance Software
If you're an insurer or a licensed intermediary, IRDAI expects more than good intentions on cybersecurity — it expects proof. Sigmify GRC gives you that: SIEM-backed risk tracking, audit readiness support, and a compliance checklist that updates as the rules do.
6 hrs
to report cyber incidents to CERT-In, with IRDAI informed
3 tiers
security-exception approval: CISO → ISRMC → Board
4×/yr
ISRMC meetings, now required quarterly
6 mo
external grey/white-box penetration testing cadence
Quick answers
The Facts You Need Before Anything Else
The 6-Hour Reporting Window
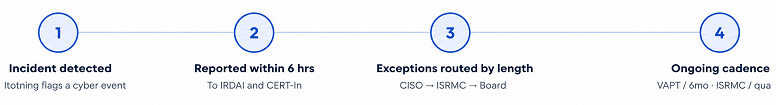
If you detect a cyber incident, the clock starts immediately: both IRDAI and CERT-In need to know within 6 hours, down from the old 24-hour window.
Who Must Appoint a CISO
Insurers, and in most cases larger licensed intermediaries, need one on staff. Since the 2026 update, that person reports independently of IT and can’t be handed business targets.
Scope Reaches Beyond Insurers
Brokers, corporate agents, insurance marketing firms and web aggregators are all in scope too, and the 2026 update pulls Foreign Reinsurance Branches in explicitly.
DPDP Alignment Is Now Built In
It is. Insurers now have to sort information assets into tiers (public, internal, restricted, confidential) and dual-tag anything personally identifiable, in line with the Digital Personal Data Protection Act.
The regulation
The IRDAI Information and Cyber Security Guidelines, 2026
IRDAI has been tightening its expectations on IT governance, cybersecurity, and operational oversight for a few years now — first through the 2023 guidelines, now further through the 2026 update.
- Insurers and intermediaries must show structured, proactive risk management, backed by SIEM monitoring and HRM logs.
- The guidelines now require clear alignment with DPDP requirements.
- In practice, that means a working checklist across your systems and logs — not a policy document sitting in a drawer.
WHAT CHANGED
Beyond the 2023 Baseline
IRDAI updated its Information and Cyber Security Guidelines in April 2026, applying across insurers, Foreign Reinsurance Branches, and intermediaries:
- CISOs now sit outside the IT function and can’t be given business targets.
- Exceptions are routed by length: CISO for shorter ones, ISRMC for medium-length ones, Board for anything past 12 months.
- ISRMC meetings move from twice a year to quarterly.
- DPDP alignment is now explicit, including tiered classification of information assets.
WHO IT APPLIES TO
Insurers, FRBs, and Intermediaries Alike
Insurers, Foreign Reinsurance Branches, and intermediaries are all covered by the update. As the 2026 requirements take effect, Sigmify GRC’s checklist and control library get updated to match, so your team isn’t stuck manually reconciling two versions of the framework.
Deadlines & exception tiers
IRDAI 2026 Deadlines, Owners, and Exception Tiers
The 2026 update attaches concrete deadlines and approval tiers to several requirements. Sigmify GRC tracks each of these automatically against your entity's compliance calendar.
| Requirement | Deadline / cadence | Owner |
|---|---|---|
| VAPT (vulnerability assessment and penetration testing) | Every 6 months, grey/white-box testing | CISO / Security team |
| High-risk vulnerability remediation | Within 30 days of identification | CISO / Security team |
| All-severity vulnerability remediation | Within 60 days of identification | CISO / Security team |
| Audit report submission (insurers) | Within 90 days of fiscal year-end | Compliance / CISO |
| Audit compliance report (intermediaries) | Within 30 days | Compliance |
| ISRMC meetings | Quarterly (up from twice-yearly) | ISRMC |
| Exception approval — up to 3 months | CISO sign-off | CISO |
| Exception approval — 3 months to 1 year | ISRMC review | ISRMC |
| Exception approval — beyond 1 year | Board + risk analysis | Board |
| Cyber incident reporting | Within 6 hours of detection | CISO / Incident response |
IRDAI expects insurers to run regular internal audits and periodic VAPT cycles as part of demonstrating ongoing, proactive risk management — not a one-time certification.
AT A GLANCE
The IRDAI Compliance Cycle
Why this can't stay a spreadsheet exercise
Scattered Tracking Is
Exactly What an Audit Finds
Compliance work tends to end up scattered: different teams, manual tracking, a handful of disconnected tools. That makes it hard to:
- Stay on top of deadlines
- Keep controls current
- Correlate events across systems
- Pull together an audit-ready trail when someone actually asks for one
Sigmify GRC replaces that patchwork with a compliance checklist library of domains and controls mapped to IRDAI requirements, updated for 2026, configurable frequencies and lead times, automated evidence tracking, and clear ownership across teams. Audits and VAPT cycles stop being an annual scramble and become part of the normal rhythm of work.
Dashboards & Risk Scorecards
Real-time dashboards and risk scorecards, backed by SIEM data, give you a live read on your posture instead of a quarterly guess.
Reduced Reputational & Penalty Risk
Solid, demonstrable compliance lowers reputational risk and helps you avoid penalties, so the tighter 2026 deadlines feel routine rather than a scramble.
Operational-to-Board Visibility
Everyone from the operational team up to the board gets visibility into compliance posture, including the tiered exception-approval and board-accountability pieces the 2026 update introduced.
The Sigmify GRC approach
Built Around How IRDAI Actually Assigns Accountability
GOVERNANCE
Governance, Mapped to IRDAI’s Own Domains
Policy and governance checklist templates come pre-built and mapped to IRDAI’s domains.
- Role-based workflow routing and evidence sign-off tracking for CISO-level accountability
- Built for the CISO’s 2026 independence — no business targets, no reporting through IT
MONITORING
Compliance Cycles Wired to Live Signals
Checklist cycles are configurable, with automated evidence tracking.
- Draws on SIEM-integrated event correlation and real-time work queues
- Risk signals feed straight into the compliance cycle instead of living in a separate system
INCIDENT RESPONSE
Built Around the 6-Hour Window Itself
Task workflows are time-bound, built around the 6-hour reporting window to both IRDAI and CERT-In.
- Escalation paths and audit trail capture designed around the window itself, not just the deadline
- Evidence pulled in from SIEM events and real-time work queues along the way
AUDIT READINESS
Board Visibility, Without the Raw Evidence Dump
Third-party evidence collection gets assigned across teams.
- Dashboards, risk scorecards, and audit readiness reporting for board-level visibility
- Oversight without requiring the board to dig through raw evidence themselves
Requirement to capability
Every IRDAI Requirement, Matched to a Capability
Sigmify GRC maps directly to IRDAI's core requirement areas — nothing covered by implication.
| IRDAI requirement area | How Sigmify GRC supports it |
|---|---|
| Board-approved information & cyber security policy | Pre-built policy and governance checklist templates mapped to IRDAI domains |
| CISO-level reporting and accountability | Role-based workflow routing and evidence sign-off tracking |
| Risk assessment and treatment | Configurable compliance checklist cycles with automated evidence tracking |
| Security monitoring and incident detection | SIEM-integrated event correlation and real-time work queues |
| Incident reporting within 6 hours (to IRDAI & CERT-In) | Time-bound task workflows with escalation and audit trail capture |
| Vendor and outsourcing oversight | Responsibility assignment across teams for third-party evidence collection |
| Internal audit and inspection readiness | Dashboards, risk scorecards, and board-level audit readiness reporting |
Stay ahead of the IRDAI 2026 guidelines
Know how Sigmify GRC's IRDAI compliance software helps you stay compliant — including the 6-hour incident reporting deadline and DPDP alignment requirements.