
SEBI CSCRF Compliance Software for SEBI-Regulated Entities
SEBI's Cybersecurity and Cyber Resilience Framework (CSCRF) sets out how SEBI-regulated entities must build and prove cyber resilience. Sigmify GRC automates that proof — SIEM-driven monitoring, HRM strategies, real-time risk visibility, and continuous audit-ready governance, risk, and compliance workflows, built around the Cyber Capability Index.
5
CSCRF applicability tiers
22
SEBI-regulated entity categories covered
5
CERT-In cyber resiliency goals
Twice yearly
Audit cadence for MIIs & Qualified REs
Applicability
Every Tier Has a Different Bar to Clear
SEBI CSCRF applicability extends across 22 categories of SEBI-regulated entities, graded into five tiers — most notably stock brokers, depository participants, and stock exchanges, alongside mutual funds & AMCs. Obligations, SOC requirements, and audit frequency scale with tier rather than applying uniformly.
| Tier | Example entities | Cyber Capability Index | SOC requirement | Audit frequency |
|---|---|---|---|---|
| Market Infrastructure Institutions | Stock exchanges, depositories, clearing corporations | 3rd-party, every 6 months | Dedicated/managed SOC | Twice yearly |
| Qualified REs | Large brokers, AMCs above client/AUM thresholds | Annual self-assessment | SOC integration | Twice yearly |
| Mid-Size REs | Mid-tier brokers, AMCs (internet/algo trading) | Self-assessment as applicable | Recommended | Twice yearly (internet/algo) or once |
| Small-Size REs | Smaller brokers, depository participants | Self-assessment as applicable | Lightweight monitoring | Once yearly |
| Self-Certification REs | Smallest-scale REs | Self-certification | Not mandated | Exempt — CERT-In VA + self-certification |
Framework foundation
Five Goals Set by CERT-In
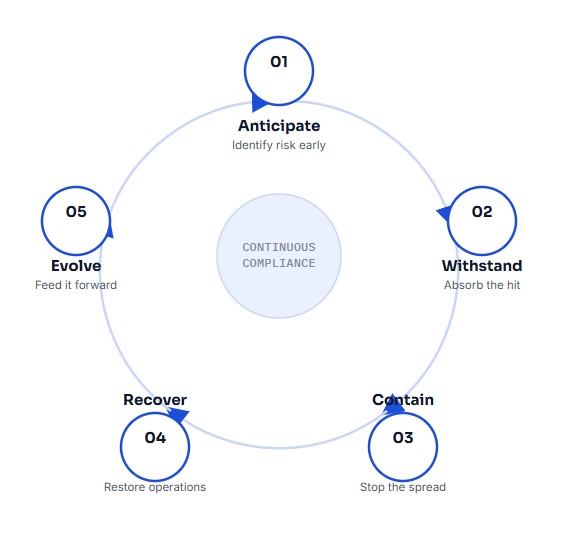
The CSCRF isn't a checklist of isolated controls — every requirement in it maps back to one of five cyber resiliency goals. Sigmify GRC maps controls and dashboards to each goal directly.
01
Anticipate
Identify risk before it’s exploited.
02
Withstand
Absorb an attack without losing function.
03
Contain
Stop an incident from spreading.
04
Recover
Restore operations to a known-good state.
05
Evolve
Feed every incident back into the program.
Why the cycle repeats
One Continuous Loop, Not a Once-a-Year Exercise
The five CERT-In goals aren't a sequence you finish. They feed each other in a loop: what you learn while recovering from an incident becomes next quarter's anticipation, and Sigmify GRC keeps every stage fed from the same live SIEM and HRM data instead of five separate spreadsheets.
Why this can't wait for audit season
Cyber Resilience Is Assessed Continuously, Not Once a Year
An audit finding and an incident-response gap tend to surface the same underlying weakness: controls that only get attention right before they're checked. Policy, risk management, data security, SOC, audits, defense fine-tuning, and incident response draw on the same SIEM and HRM signal, so Sigmify GRC runs all seven off one continuously current data foundation instead of reassembling evidence ahead of each deadline.
Risk visibility that doesn't go stale
SIEM/HRM-correlated risk management continuously assesses risk, identifies critical assets, and defines acceptable risk levels from correlation engines, vulnerability tools, and threat intel feeds.
One SOC, feeding every workstream
Centralized log management, event correlation, and threat detection feed red-team tuning and incident response from the same data — not separate tools per requirement.
Audit evidence, always current
Automated evidence collection and continuous compliance tracking mean audit readiness doesn’t get rebuilt from scratch before each cycle.
Requirement to capability
What CSCRF Requires, Mapped to What Sigmify GRC Does
Every CSCRF requirement traces to a specific Sigmify GRC capability — nothing is covered by implication.
| SEBI CSCRF requirement | Sigmify GRC capability |
|---|---|
| Board-approved cybersecurity policy | Policy library with senior-management sign-off workflows and version history |
| Risk management & critical asset identification | SIEM/HRM-correlated risk register with continuous re-assessment |
| Data security (encryption, access controls) | Real-time anomaly and unauthorized-access monitoring across SIEM and HRM sources |
| SOC: centralized log management, event correlation | SIEM/HRM-integrated SOC workflows with real-time incident monitoring |
| Regular cybersecurity audits | Automated evidence collection and continuous audit-readiness tracking |
| Ongoing adversarial testing of defenses | Folded into our continuous detection-and-response fine-tuning process, not run as a standalone exercise |
| Incident response & cyber crisis management | Automated incident workflows and real-time regulatory reporting replace this content |
Deadlines
Tracking a Compliance Date That Keeps Moving
SEBI's CSCRF circular has been amended and extended multiple times since its original issuance, including the SBOM compliance deadline, which has been extended for many REs. Deadlines are tier-specific and subject to further amendment — confirm the current one for your tier before your next audit cycle.
CIRCULAR TRACKING
Every Amendment, Tracked Automatically
Sigmify GRC tracks every circular update automatically, so compliance deadline exposure never depends on manually monitoring SEBI’s circular calendar, and its control library is updated as SEBI issues new guidance.
CONTROL LIBRARY
Checklists That Update With the Framework
Sigmify GRC defines and manages updates to control libraries and checklists, including your SEBI CSCRF checklist — so a circular amendment doesn’t mean rebuilding tracking from scratch.
Common questions
Before You Start
The framework outlines guidelines for SEBI-regulated entities — including stock brokers, mutual funds/AMCs, and stock exchanges — to improve cybersecurity and build lasting cyber resilience.
Sigmify GRC’s operational platform performs SEBI CSCRF SOC requirements and audit checklist tasks, and records evidence for every requirement — from SOC monitoring to incident response — inside the same governance, risk, and compliance workflows used across other frameworks.
Sigmify GRC improves visibility into your compliance program with dashboards mapped to each CERT-In cyber resiliency goal — anticipate, withstand, contain, recover, and evolve — rather than a generic control list.
Know your tier. Know your gap.
See how Sigmify GRC helps you stay compliant with SEBI CSCRF and other regulatory frameworks.