
Simplify HIPAA compliance with one unified framework for Privacy, Security & Breach Notification
Sigmify GRC discovers protected health information (PHI) across your systems, automates controls and evidence collection, and keeps covered entities and business associates audit-ready — continuously, not just at audit time.
Key Takeaways
- One framework, three rules. Sigmify GRC’s Unified Compliance Framework centralizes Privacy, Security, and Breach Notification Rule management instead of tracking each separately.
- PHI is discovered automatically. Sigmify’s PHI discovery and classification software finds and classifies PHI across systems and maintains data inventories and flow maps.
- Every vendor is covered by a BAA. A Business Associate Agreement governs how any vendor handling PHI must comply with HIPAA, managed through dedicated BAA software.
- Compliance status updates in real time. A live dashboard shows compliance posture, control effectiveness, audit logs, and incident status — continuously, not just at audit time.
- Breach response follows the Breach Notification Rule. Incidents are detected, investigated, and managed with a built-in breach risk assessment tool and notification workflows.
What HIPAA Compliance Software Does
Helps covered entities and business associates operationalize the requirements of HIPAA — including the Privacy, Security, and Breach Notification Rules — through structured controls, automated workflows, and audit-ready evidence.
Who Needs to Comply with HIPAA
maintain, or transmit protected health information (PHI).
At a Glance
The Three HIPAA Rules, At a Glance
Sigmify GRC aligns with all three HIPAA rules — Privacy, Security, and Breach Notification — covering Privacy Rule compliance, Security Rule safeguards, and breach notification.
| HIPAA Rule | What It Requires | How Sigmify GRC Supports It |
|---|---|---|
| Privacy Rule | Appropriate use and disclosure of PHI, including minimum necessary requirements, patient rights, and authorization tracking | HIPAA Privacy Rule compliance software managing minimum necessary requirements, patient rights, and authorization tracking |
| Security Rule | Administrative, physical, and technical safeguards which when identified through a HIPAA risk assessment covered access controls, encryption, audit logs, and system integrity. | Implementation and monitoring of the Security Rule safeguards identified by a HIPAA risk assessment |
| Breach Notification Rule | Detecting, investigating, and managing incidents involving PHI, including a breach risk assessment aligned with the rule | HIPAA breach notification software with a built-in breach risk assessment tool aligned with the rule |
Why It Matters Now
Three Rules, Run as One Program
A HIPAA program run rule by rule creates the exact gap an audit finds — controls tracked in separate places with no single view of where things stand. Sigmify GRC closes that gap:
One Framework, Not Three Separate Tracks
A Unified Compliance Framework replaces three disconnected trackers with one system.
- Centralizes Privacy, Security & Breach Notification management
- Maps safeguards, policies & controls to enterprise systems
- Runs continuous compliance monitoring & readiness
Compliance That Follows PHI Past Your Own Walls
HIPAA risk extends to every vendor and business associate that touches PHI.
- Ensures vendors handling PHI comply with HIPAA
- Managed through dedicated BAA software
A Dashboard That Never Stops Checking
Replaces the audit-day snapshot with an always-on view.
- Tracks compliance posture & control effectiveness
- Surfaces audit logs & incident status
- Updates continuously, across healthcare systems
What HIPAA Compliance Actually Means
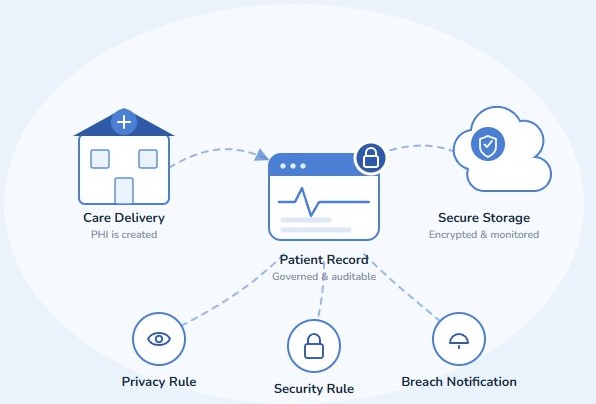
From the Exam Room to Secure Storage — Every Step Governed
Protected health information moves from care delivery, through a governed record, into secure storage — with all three HIPAA rules watching every step.
Compliance Capabilities
How Sigmify GRC Supports Every HIPAA Rule
Each capability below is self-contained — built to answer the underlying question fully, not just gesture at it.
One Framework, Three Rules, No Gaps Between Them
A Unified Compliance Framework centralizes requirements across multiple rules — for HIPAA, the Privacy, Security, and Breach Notification Rules — instead of managing each as a separate effort.
- Centralizes HIPAA management across all three rules
- Maps safeguards, policies & controls to enterprise systems
- Supports continuous compliance monitoring & audit readiness
Knowing Every Place PHI Actually Lives
A PHI data inventory and flow map documents how Protected Health Information (PHI) moves across an organization’s systems.
- Automatically discovers & classifies PHI across systems
- Maintains data inventories & flow maps
- Shows how PHI is created, received, maintained & transmitted
Use and Disclosure, Kept Inside the Lines
The Privacy Rule governs the appropriate use and disclosure of PHI, including minimum necessary requirements, patient rights, and authorization tracking.
- Ensures appropriate use & disclosure of PHI
- Manages minimum necessary requirements
- Tracks patient rights & authorizations
Safeguards Built From Your Own Risk Assessment
The Security Rule requires administrative, physical, and technical safeguards, identified through a HIPAA risk assessment.
- Implements & monitors safeguards from a risk assessment
- Tracks access controls & encryption
- Maintains audit logs & system integrity
Access, Amendments, Accounting — Answered on Time
HIPAA guarantees patients the right of access, the right to request amendments, and the right to an accounting of disclosures.
- Automates workflows for access, amendment & disclosure requests
- Ensures timely response & compliance
Compliance Status, As It Happens
A real-time HIPAA compliance monitoring dashboard shows compliance posture, control effectiveness, audit logs, and incident status across healthcare systems.
- Tracks compliance posture & control effectiveness
- Surfaces audit logs & incident status
- Updates in real time, not just at audit time
Vendor Risk, Bound by Contract
A Business Associate Agreement (BAA) governs how a vendor handling PHI must comply with HIPAA.
- Ensures vendors handling PHI comply with HIPAA requirements
- Manages BAAs through dedicated software
- Monitors third-party compliance on an ongoing basis
How does HIPAA audit software support internal and external audits?
Sigmify’s HIPAA audit software supports both internal and external audits.
- Automated evidence collection
- Documentation aligned with regulatory expectations
- Traceability across internal & external audits
From Detection to Notification, Without the Guesswork
Managing a HIPAA incident or breach means detecting, investigating, and managing incidents involving PHI.
- Built-in breach risk assessment tool
- Aligned with the Breach Notification Rule
- Notification workflows for individuals, HHS & media, where required
Every Box HIPAA Actually Asks You to Check
A complete HIPAA checklist confirms core controls across all three rules — each imposes obligations the others don’t cover.
Privacy Rule
- Minimum necessary use and disclosure policy documented and enforced
- Patient authorization and consent tracking in place
- Notice of Privacy Practices current and distributed
Security Rule
- Administrative, physical, and technical safeguards mapped to a current risk assessment
- Access controls, encryption, and audit logging active on all systems handling PHI
- Workforce security training completed and documented
Breach Notification Rule
- Breach risk assessment process defined and tested
- Notification workflows ready for individuals, HHS, and media (where required)
- Business Associate Agreements in place for every vendor handling PHI
Comply with HIPAA with Confidence
Protect patient information, reduce compliance risk, and demonstrate accountability — with one unified HIPAA compliance platform for healthcare organizations and their partners.