Skip to content
sigmify-logosigmifygrc-logo
Request a Demo DPDPA Assessment
  • Challenge
    • Standards
    • Industry
      • BFSI
        • RBI
        • SEBI
        • IRDAI
        • DPDPA
      • Healthcare & Pharma
        • DPDPA
    • Regulation
      • GDPR
      • CCPA
      • PDPA
      • HIPAA
  • Solution
    • Products
      • Compliance & IT Governance
      • Assessments
      • Data Discovery, Classification and Mapping
      • Consent Management
      • Risk Management
      • Vendor Risk Management
      • Audit Management
      • Breach and Exceptions Management
      • Integrations
    • Features
    • Services
  • Sigmify AI
    • Beacon Scanner
    • Beacon Audit
    • Beacon Priorities
    • Beacon Extract
  • Resources
    • Case Studies
    • Blogs
    • Broadcast
    • News
      • All Announcements
        • Events & Conferences
        • Product Updates & Releases
  • About Us
    • Our Team
Menu Close
  • Challenge
    • Standards
    • Industry
      • BFSI
        • RBI
        • SEBI
        • IRDAI
        • DPDPA
      • Healthcare & Pharma
        • DPDPA
    • Regulation
      • GDPR
      • CCPA
      • PDPA
      • HIPAA
  • Solution
    • Products
      • Compliance & IT Governance
      • Assessments
      • Data Discovery, Classification and Mapping
      • Consent Management
      • Risk Management
      • Vendor Risk Management
      • Audit Management
      • Breach & Exceptions Management
      • Integrations
    • Features
    • Services
  • Sigmify AI
    • Beacon Scanner
    • Beacon Audit
    • Beacon Priorities
    • Beacon Extract
  • Resources
    • Case Studies
    • Blogs
    • Broadcast
    • News
      • All Announcements
        • Events & Conferences
        • Product Updates & Releases
  • About Us
    • Our Team
Read more about the article Ensuring Data Privacy Verifying @ scale

Ensuring Data Privacy Verifying @ scale

  • Post published:March 30, 2026
  • Post author:Manoj Sinha

“Intent” in the IDEA framework for Data PrivacyIt was the dawn of May 29, 1453, a Tuesday, when the confident defenders of Constantinople were blindsided by a charge from the…
Continue ReadingEnsuring Data Privacy Verifying @ scale
Read more about the article Behind the Screens – GRC Chaos due to Systems and Processes

Behind the Screens – GRC Chaos due to Systems and Processes

  • Post published:December 3, 2025
  • Post author:Manoj Sinha

Operational Challenges in Implementing Tech GRC In an earlier post I talked about the why organizations face difficulties as they implement a sound Technology GRC program. As I mentioned, there…
Continue ReadingBehind the Screens – GRC Chaos due to Systems and Processes
Read more about the article Is the Human Firewall Up? GRC’s People Issues

Is the Human Firewall Up? GRC’s People Issues

  • Post published:November 12, 2025
  • Post author:Manoj Sinha

As I have mentioned earlier in my blogs on "Cyber attacks - What you cant see can hurt you" , "urgent is Loud and Important is quiet" and "Threats change faster…
Continue ReadingIs the Human Firewall Up? GRC’s People Issues
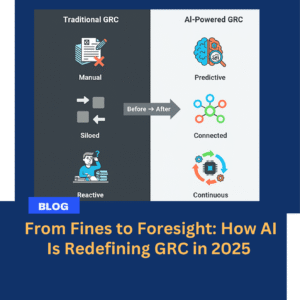
Read more about the article From Fines to Foresight: How AI Is Redefining GRC in 2025 (Series 1)

From Fines to Foresight: How AI Is Redefining GRC in 2025 (Series 1)

  • Post published:October 28, 2025
  • Post author:Manas Khandwal

“Could this have been prevented?” That’s the haunting question every technology leader and compliance officer asks after a major failure — when systems go down, customer data is exposed, or…
Continue ReadingFrom Fines to Foresight: How AI Is Redefining GRC in 2025 (Series 1)
Read more about the article The Technology GRC maze: What a tangled web we have woven

The Technology GRC maze: What a tangled web we have woven

  • Post published:September 30, 2025
  • Post author:Manoj Sinha

Why manage technology Governance Risk and Compliance? And how? Because to err is human, to really mess things up requires a computer. I am sure you have heard the Paul…
Continue ReadingThe Technology GRC maze: What a tangled web we have woven
Read more about the article Complexity of a GRC Program – Are You Losing 4% of Your Workforce Without Noticing?

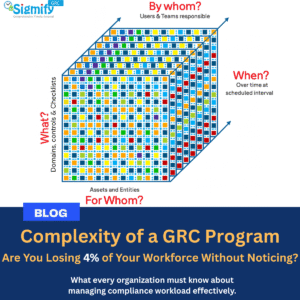
Complexity of a GRC Program – Are You Losing 4% of Your Workforce Without Noticing?

  • Post published:September 23, 2025
  • Post author:Manoj Sinha

4% of your workforce. On an ongoing basis! This is what GRC tasks will exact from you if they are not managed well. This is the magnitude of ‘things’ that…

Continue ReadingComplexity of a GRC Program – Are You Losing 4% of Your Workforce Without Noticing?
  • Go to the previous page
  • 1
  • 2
  • 3
  • 4
  • Go to the next page

Categories

  • Broadcast
  • Case Study
  • Compliance and Risk Management
  • Events & Conferences
  • Governance
  • News
  • Product Updates & Releases

Recent Posts

  • From Policies to Practice: Implementing Data Privacy Compliance Using a GRC Platform
    From Policies to Practice: Implementing Data Privacy Compliance Using a GRC Platform
    September 9, 2026/
    0 Comments
  • Why Manufacturing Industry Needs a GRC Platform for Data Privacy Compliance?
    Why Manufacturing Industry Needs a GRC Platform for Data Privacy Compliance?
    August 5, 2026/
    0 Comments
  • Why Manufacturing Industry Needs to be Aware of Digital Personal Data Privacy Laws?
    Why Manufacturing Industry Needs to be Aware of Digital Personal Data Privacy Laws?
    July 20, 2026/
    0 Comments
Resource

Contact us: sales@sigmify.com

Privacy Statement | Security Statement


Copyright 2026 - Sigmify